Intelligence Brief
Microsoft's Security Theater
Federal reviewers spent five years trying to verify whether Microsoft's government cloud was secure. They never got the answers they needed. The system was approved anyway.
A major new ProPublica investigation found that federal cyber reviewers spent five years trying to verify whether Microsoft’s Government Community Cloud High, the cloud service handling some of America’s most sensitive information, was secure. The service stores Justice Department law enforcement records and is used by defense contractors like Boeing. Reviewers never received the answers they needed, yet the government approved the system anyway.
The broader context is critical. Microsoft products were already at the center of two major cyberattacks against the U.S. government in recent years. Russian hackers exploited a Microsoft weakness to penetrate federal agencies, including the National Nuclear Security Administration. Chinese state-sponsored hackers then infiltrated Microsoft’s government cloud, stealing data from the Secretary of Commerce, the U.S. Ambassador to China, and other senior officials. That breach happened while auditors were still reviewing a related product that was eventually approved — and it was alarming enough that they terminated the process and had to start over.
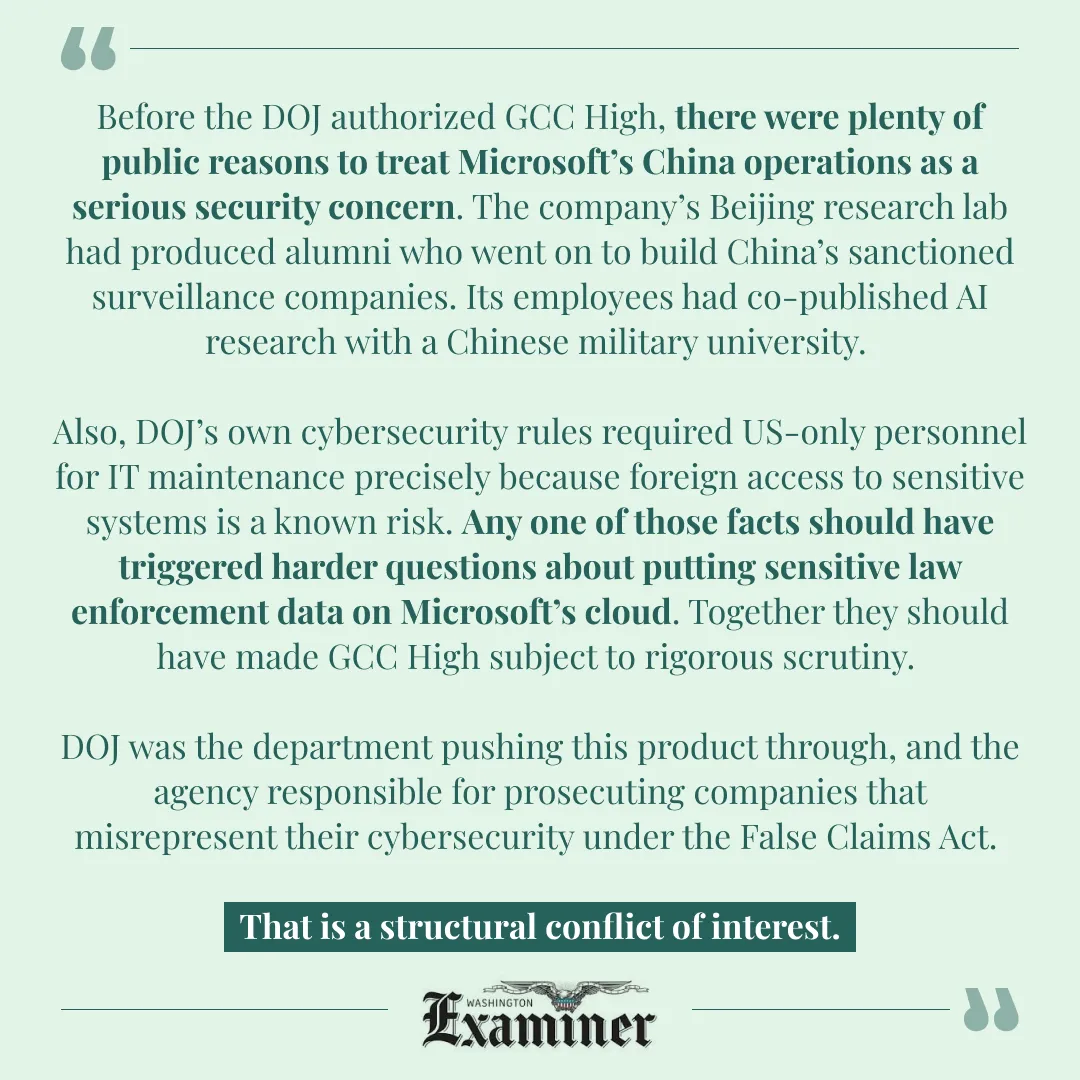
Microsoft’s troubling past warranted serious scrutiny, but the system buckled under industry pressure. As the Washington Examiner highlighted, the DOJ official who first authorized the product, and who later pressured auditors to “get this thing over the line,” was subsequently hired by Microsoft. And the Deputy Attorney General who launched the initiative to prosecute cybersecurity fraud by government contractors — but did not apply that scrutiny to Microsoft — now serves as the company’s President of Global Affairs. The revolving door did not just fail to prevent this outcome. It helped produce it.
Federal regulators must begin treating government cybersecurity with the seriousness it demands. As I told the Examiner, for too long, effective scrutiny has been absent.
This is not security. This is security theater.
As a former NSA computer scientist put it to ProPublica, federal agencies have the information they need to know — and act — better. It’s past time they do.
In This Briefing
Get the next brief in your inbox.
Subscribe to Briefings →